
How End-to-End Encryption Secures Smart Home Video on Device Silicon Before the Cloud
As major smart home brands push default end-to-end encryption, the technical reality of securing video on low-power cameras reveals a complex trade-off between privacy and convenience.
By Tariq Nasser
Share this story
In short
- True end-to-end encryption (E2EE) ensures only the user's device holds the decryption keys, blinding the cloud provider to the video feed.
- Implementing E2EE on battery-powered cameras requires specialized 'lightweight cryptography' to avoid draining the device.
- NIST recently standardized the Ascon algorithm specifically to solve the processing constraints of small IoT devices.
On August 26, 2026, Amazon's Ring flipped a switch that fundamentally altered how millions of front doors are monitored, introducing "TAKE" to make end-to-end encryption (E2EE) the default standard rather than a buried opt-in setting. The move signals a broader industry pivot, but it also highlights a persistent gap between marketing claims and cryptographic reality.[6]
For years, smart home marketing has leaned heavily on phrases like "bank-level security" or "military-grade encryption." In reality, this usually just meant the video stream was encrypted while traveling to the company's cloud—known as encryption in transit—and while stored on their servers. The data was secure from outside interception, but the manufacturer retained the ultimate ability to unlock it.[9]
Under those legacy models, the company held the decryption keys. If a server was breached, a rogue employee accessed the backend, or a legal warrant was served, the video could be viewed in plaintext by third parties without the camera owner ever knowing. This architecture prioritized convenience and cloud processing over absolute privacy.[7][10]
True end-to-end encryption removes the middleman entirely. In a genuine E2EE architecture, the video feed is encrypted locally on the camera's own silicon before it ever hits the Wi-Fi network, ensuring the cloud provider remains completely blind to the data payload.[8]
The cryptographic keys required to unlock that footage are generated and stored exclusively on the user's enrolled mobile device. The cloud merely acts as a courier, shuffling scrambled data packets from the camera to the phone without ever possessing the mathematical means to read them.[5]
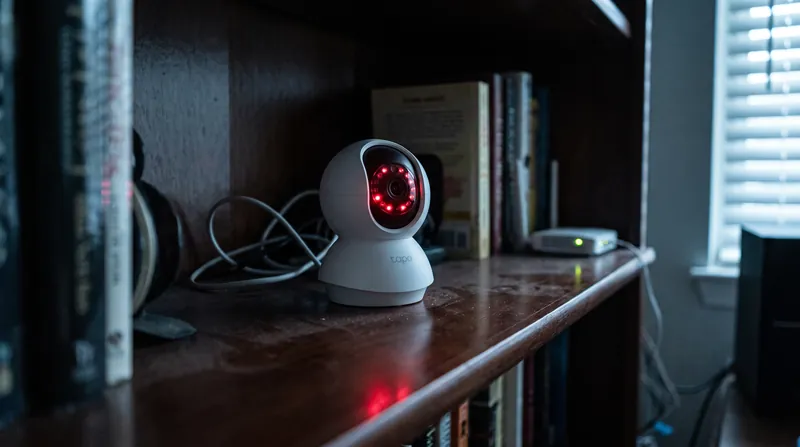
Implementing this on a smartphone is trivial, but executing it on a battery-powered doorbell camera is a severe engineering challenge. Video encoding is computationally expensive, and adding real-time cryptographic scrambling drains small batteries rapidly while generating excess heat that degrades hardware.[1]
This hardware bottleneck forced the industry to look beyond traditional algorithms like AES-256. In August 2025, the National Institute of Standards and Technology (NIST) finalized its "Lightweight Cryptography" standard, specifically designed for constrained Internet of Things devices that lack the processing power of a modern smartphone.[2]
The resulting publication, SP 800-232, crowned the Ascon family of algorithms as the new benchmark for authenticated encryption on microcontrollers. Ascon requires significantly less memory and processing power, allowing a cheap camera to encrypt 1080p video on the fly without dying in a week.[1]
The push for E2EE is also being codified into broader interoperability standards. The Matter protocol, which aims to unify smart home ecosystems, mandates strict local-network security baselines that prevent devices from communicating in plaintext even within the home network, raising the floor for the entire industry.[3]
However, the transition to E2EE introduces a massive functional trade-off: if the cloud cannot see the video, the cloud cannot process it. Features that consumers have come to expect—like AI-driven package detection, facial recognition, or animal tracking—traditionally rely on massive server-side neural networks analyzing the unencrypted feed.[9]
To maintain these features under E2EE, manufacturers must move the artificial intelligence directly onto the camera itself, a concept known as edge processing. This requires more expensive silicon in the device, pushing up the retail cost of secure cameras and forcing a hardware upgrade cycle for consumers who want both privacy and smart alerts.[4]
Another friction point is key management. If a user wants to share camera access with a spouse, the system must securely provision a new key for the second device without routing it through the manufacturer's servers, a process that often requires both devices to be physically near each other during setup or relies on complex public-key infrastructure.[5]
This complexity explains why companies like Ring previously relegated E2EE to an "advanced" toggle that disabled features like viewing footage on web dashboards, smart displays, or third-party integrations. Making it the default requires solving these user experience hurdles without compromising the underlying math.[7]
How can a consumer verify that a camera is truly E2EE? Independent security audits and open-source cryptographic libraries are the only reliable proofs. When a company claims E2EE but refuses to publish whitepapers detailing their key exchange protocol, security researchers remain highly skeptical of the implementation.[9][10]
As lightweight cryptography becomes ubiquitous and edge AI chips drop in price, the technical excuses for avoiding E2EE are evaporating. The smart home is slowly shifting from a model of blind trust in cloud providers to one of mathematical certainty, provided consumers are willing to navigate the initial setup friction.[10]
Jargon, explained
- End-to-End Encryption (E2EE)
- A secure communication process that prevents third parties from accessing data while it's transferred from one end system or device to another.
- Encryption in Transit
- Securing data only while it travels across a network, meaning it is decrypted once it reaches the company's servers.
- Lightweight Cryptography
- Encryption algorithms designed specifically for devices with limited processing power, memory, and battery life, such as smart home sensors.
- Ascon
- A family of authenticated encryption algorithms selected by NIST as the standard for securing constrained Internet of Things devices.
- Edge Processing
- Performing data analysis and AI tasks directly on the local device (the "edge") rather than sending the data to a centralized cloud server.
Common questions
Can the manufacturer see my video if I use E2EE?
No. With true end-to-end encryption, the manufacturer's servers only handle scrambled data. They do not possess the cryptographic keys required to view the footage.
Why do some features break when E2EE is turned on?
Features like cloud-based package detection or facial recognition require the server to analyze the unencrypted video. If the cloud cannot see the video, it cannot process these alerts unless the camera has a built-in edge AI chip.
What happens if I lose my phone?
Because the decryption key is stored on your device, losing your only enrolled device can result in the permanent loss of access to your encrypted video history, unless you have generated a secure backup passphrase.
Does E2EE drain camera batteries faster?
Historically, yes. However, new lightweight cryptography standards like Ascon are specifically designed to minimize the processing power and battery drain required to encrypt video on small devices.
Competing readings
Privacy Advocates
Argue that true E2EE is the only acceptable standard for indoor and residential cameras.
Privacy researchers emphasize that the home is a uniquely sensitive environment, and any architecture that allows a third-party cloud provider to hold decryption keys is inherently flawed. They point to historical incidents of rogue employees accessing feeds and the increasing volume of warrantless police requests as proof that encryption in transit is insufficient. For this camp, the minor inconveniences of key management are a necessary trade-off for mathematical certainty against surveillance.
Smart Home Manufacturers
Balance the demand for privacy with the technical constraints of device cost and user experience.
Hardware makers face the practical challenge of selling cameras that consumers actually want to use. They argue that while E2EE is the ideal, it breaks popular features like cloud-based AI alerts and web dashboard viewing. Furthermore, upgrading silicon to support edge processing and lightweight cryptography increases the manufacturing cost of the device. Their goal is to implement E2EE without alienating users who expect seamless sharing and intelligent notifications.
Law Enforcement
Express concern over the loss of digital evidence in criminal investigations.
While not explicitly represented in the technical documentation, law enforcement agencies have historically pushed back against default E2EE. When a camera manufacturer holds the keys, police can serve a warrant directly to the company to obtain footage of a crime. Under a true E2EE model, the company cannot comply even if they want to, forcing investigators to seize the physical smartphone of the suspect or victim to access the video.
- Privacy Advocates
- Argue that true E2EE is the only acceptable standard for indoor and residential cameras, eliminating the risk of cloud breaches.
- Smart Home Manufacturers
- Balance the demand for privacy with the technical constraints of battery life, device cost, and the user desire for AI-driven features.
- Standards Bodies
- Focus on developing lightweight, interoperable cryptographic protocols that allow low-power devices to secure data efficiently.
Perspectives this story doesn't cover
- Emergency First Responders
- Law Enforcement Agencies
Sources
Source coverage
10 outlets
3 viewpoints surfaced




- [1]NIST CSRCStandards Bodies
SP 800-232, Ascon-Based Lightweight Cryptography Standards for Constrained Devices: Authenticated Encryption, Hash, and Extendable Output Functions
Read on NIST CSRC → - [2]NISTStandards Bodies
NIST Finalizes 'Lightweight Cryptography' Standard to Protect Small Devices
Read on NIST → - [3]Smart Home Security AuthorityStandards Bodies
Matter Protocol Security for Smart Home Devices
Read on Smart Home Security Authority → - [4]Home Security Systems AuthorityStandards Bodies
Encryption Standards for Home Security Systems
Read on Home Security Systems Authority → - [5]SignifySmart Home Manufacturers
Guarding Your Privacy: Philips Hue Secure's End-to-End Encryption
Read on Signify → - [6]Amazon NewsSmart Home Manufacturers
Ring introduces TAKE, setting a new industry standard for default encryption and control
Read on Amazon News → - [7]RingSmart Home Manufacturers
Using legacy video end-to-end encryption (E2EE)
Read on Ring → - [8]TrueConfStandards Bodies
What Is End-to-End Encryption?
Read on TrueConf → - [9]arXivPrivacy Advocates
Synthesizing Smart Home Privacy Protection Mechanisms Across Academic Proposals and Commercial Documentations
Read on arXiv → - [10]Factlen Editorial TeamPrivacy Advocates
Synthesis by Factlen editorial team
Read on Factlen Editorial Team →
More in Technology
See all →Smart Home Architecture
Why Local Smart Home Processing Eliminates Latency and Internet Dependency but Sacrifices Complex AI
9 sources
Sensor Accuracy
The Mechanism and Blind Spots of Smart Air Purifier Sensors
5 sources
Smart Home Protocols
The Sleep State Advantage: Why Zigbee and Z-Wave Sensors Outlast Wi-Fi by Years
7 sources
HVAC Automation
Smart Thermostats Save Energy via Model Predictive Control, Not Schedule Tracking
4 sources
Comments
Every angle. Every day.
Get Technology stories with full source coverage and perspective breakdowns, free every day.